In July 2026, the European Data Protection Board (EDPB) published Guidelines 02/2026 on Anonymisation for public consultation. The consultation remains open until 30 October 2026, which means the text may still change before the final version is adopted. Even at this stage, however, the draft provides a useful framework for organisations that need to assess whether information has been anonymised effectively.
What are the EDPB Guidelines 02/2026 on Anonymisation?
The purpose of the Guidelines is to clarify the concept of anonymous information and provide a practical framework for assessing whether an anonymisation process has been successful. They update the approach previously discussed by the Article 29 Working Party in its 2014 opinion on anonymisation techniques.
The technological environment has changed substantially since 2014. Artificial intelligence, search engines, public databases and analytical tools make it easier to combine information from multiple sources. As a result, information that may have appeared anonymous several years ago can now be easier to reconnect with a specific individual.
This is why anonymisation should not be treated simply as a one-time technical action. The more important question is whether a person can still be identified using means that are reasonably likely to be used in the relevant context.
Removing a name does not necessarily mean anonymisation
This is one of the most important practical conclusions for organisations working with documents.
Suppose a document has had the following information removed:
- first name
- surname
- email address
- telephone number
- identification number
At first glance, the document may appear anonymous. However, it may still contain the person’s job title, employer, town, exact date of an incident and information about a rare medical condition.
Each of these details considered separately may not identify anyone. Combined, however, they may point to one specific person.
For document anonymisation, the assessment therefore cannot stop at checking whether a name, address or national identification number has been removed. It should also consider whether the remaining information can still distinguish or identify an individual.
Three criteria for assessing effective anonymisation
The EDPB describes three criteria that help determine whether information can be considered anonymous: no record isolation, no linkage and no inference.
1. No Record Isolation
The first criterion concerns whether information relating to one specific person can still be isolated from the rest of the dataset or document collection.
Information may remain identifying even if it does not contain a name. For example, a combination such as Regional Sales Director + Szczecin + 42 years old + accident on 17 March may, in a particular organisational context, point to only one person.
This means that anonymisation should consider not only direct identifiers but also combinations of characteristics and contextual information.
2. No Linkage
The second criterion concerns whether information can be linked to another source of data. A document may contain no direct identifier and still be capable of being associated with another dataset.
Such a source might include:
- a public register
- a company website
- a customer database
- an internal HR system
- a published administrative decision
- another document
For example, removing an employee’s name may not be sufficient if the remaining job title, department and project name make it easy to identify that person through the organisation’s website. Effective anonymisation should therefore also take into account information available outside the document itself.
3. No Inference
The third criterion concerns whether information about a specific individual can be inferred from the remaining data. This is often the most difficult element of the assessment.
A document may contain no name and may not be directly linkable to another dataset, but the remaining information may still allow someone to draw conclusions about a particular individual.
For example, a report concerning a small team may disclose the salaries of five out of six employees while identifying the role of the sixth person. In some circumstances, this may make it possible to infer the sixth employee’s salary.
Anonymisation therefore requires more than searching for and removing a predefined list of personal data. Context matters.
Two ways to apply the EDPB anonymisation assessment
The EDPB also distinguishes between a contextual approach and a simplified approach. In its official overview of the draft Guidelines, the Board explains that the contextual approach reflects the full legal standard by looking at the entities that may receive or access the information and the means reasonably likely to be available to them.
The simplified approach is more conservative. It can lead an organisation to treat information as non-anonymous even where it might be anonymous for some recipients, but it may be easier to apply and can provide greater confidence that the information is genuinely anonymous.
For organisations working with documents, this distinction is important because the same file may present a different identification risk depending on who receives it, what other information they hold and what external sources they can access.
Anonymous for whom? The importance of context
One of the most important elements of the EDPB approach is that the assessment is contextual. The same information may be anonymous for one recipient while remaining identifiable for another.
For example, an organisation removes a customer number from a document before sharing it with an external researcher. The researcher may have no additional data that would allow the individual to be identified. At the same time, the organisation that prepared the document may still hold another database that makes it easy to determine which customer the document concerns.
As a result, it is not enough to ask only whether personal data has been removed from a document. Organisations should also ask who will receive the document and what additional information that recipient may reasonably have access to.
The anonymisation process itself is still subject to the GDPR
There is another important distinction. Even if the final result becomes genuinely anonymous, the anonymisation process itself is performed on personal data.
This means that the GDPR continues to apply while anonymisation is taking place. The organisation should have an appropriate legal basis for the processing under Article 6 GDPR and, where special categories of personal data are involved, should also consider the conditions set out in Article 9 GDPR.
In practice, two stages can therefore be distinguished:
- before successful anonymisation – the organisation is processing personal data;
- after successful anonymisation – the resulting information may fall outside the scope of the GDPR.
The transition between these stages should be controlled and supported by an assessment of whether the result actually meets the required anonymity standard.
Documenting the anonymisation process is increasingly important
The draft Guidelines also emphasise the importance of documenting the anonymisation process and being able to demonstrate how the assessment was performed.
In practice, organisations may document elements such as:
- how the data was anonymised
- which information was removed or modified
- which criteria were applied
- whether the effectiveness of the process was verified
- who participated in the process
- when the process was carried out
For organisations that process documents regularly, this leads to a straightforward conclusion: a repeatable and traceable anonymisation process is easier to review and defend than manually and inconsistently covering selected parts of a document.
Anonymisation may need to be reassessed over time
Anonymity should not always be treated as a permanent property of a document or dataset. New public data sources, technological developments, changes in access to internal information or other circumstances may affect whether an individual can still be identified.
For this reason, organisations should consider whether an earlier anonymisation assessment remains appropriate when the context changes. This is especially relevant when documents are stored for long periods or shared with new categories of recipients.
What do the Guidelines mean for document anonymisation?
For organisations that work primarily with documents rather than large statistical datasets, the EDPB principles can be translated into several practical questions.
Before sharing a document, organisations should consider:
- Have all direct identifiers been removed?
- Do any indirect identifiers remain that could distinguish one individual?
- Could a combination of remaining information lead to identification?
- Could the document be linked with another public or internal source of information?
- Could information about a specific person be inferred from what remains?
- Who will receive the document and what additional information might they have access to?
- Can the organisation demonstrate how the anonymisation process was performed?
These questions illustrate why professional document anonymisation increasingly requires a combination of automated classification, predefined rules, user control and process history.
How Bluur supports a structured anonymisation process
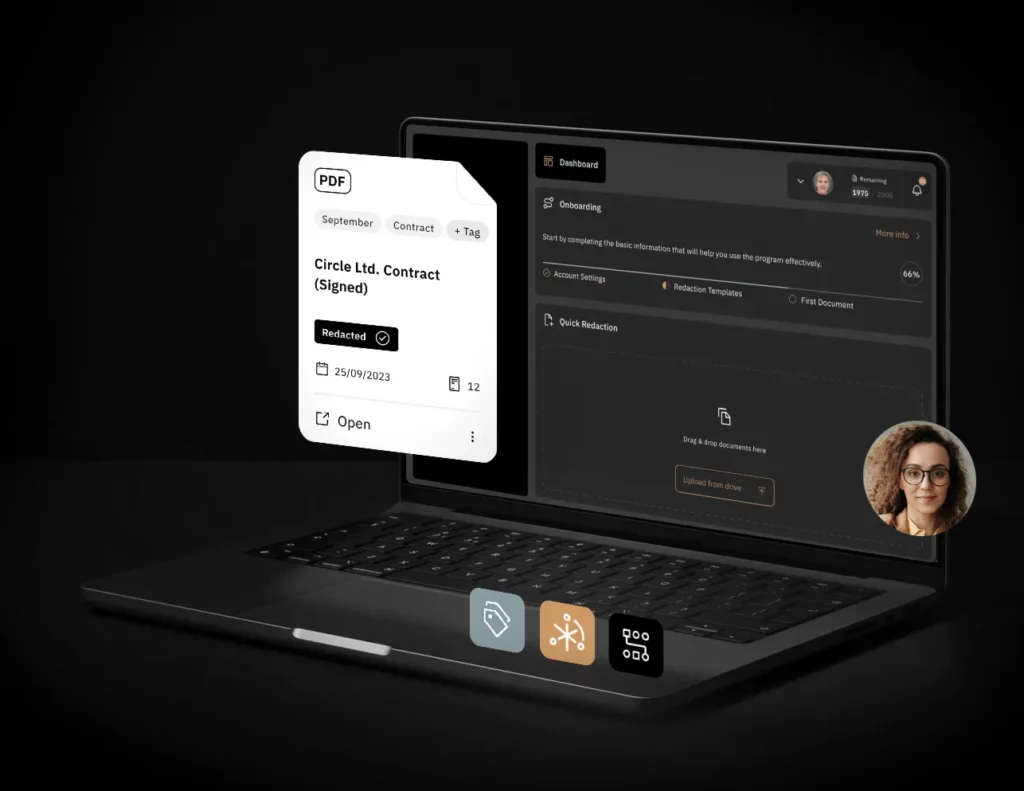
Bluur® document anonymisation is built around a workflow in which information contained in documents is first detected and classified, after which the user decides which elements should be permanently removed.
The system uses AI-based document classification to detect and categorise information contained in files. Users can then review the detected elements, correct the result, add their own redaction areas and decide which information should be anonymised.
In the context of the EDPB Guidelines, the value of this workflow lies not only in automatic detection but also in creating a repeatable process that still leaves room for human assessment of context.
Repeatable anonymisation schemes
Bluur allows organisations to use configurable redaction templates and anonymisation rules that define which categories of information should be handled in specific types of documents.
Separate configurations can be prepared for processes such as:
- contracts
- HR documentation
- medical records
- case files
- documents intended for public disclosure
- customer documentation
This reduces situations in which each employee independently decides which types of information should be removed. The system does not make a legal determination that the final document is anonymous, but it can help organisations build a more consistent and repeatable process.
Automated classification combined with human review
The EDPB framework shows why full automation of anonymisation is not always sufficient. A system may correctly detect a name, address, document number or bank account number, while a human reviewer may still need to assess whether a project name, specific job title, date of an incident or unusual combination of information could identify a person in a particular context.
Bluur therefore allows users to review detected information, add manual redaction areas and correct the result before generating the final document. This combination of automation and human verification is particularly relevant where re-identification risk depends on information that goes beyond standard data categories.
Process history and auditability
The EDPB’s focus on documentation also makes process history increasingly relevant. Bluur records operations related to document processing, helping organisations reconstruct what happened and who was involved in the workflow, depending on the permissions assigned in the system.
Such mechanisms can support internal accountability and make the anonymisation process easier to review. However, an activity log or anonymisation certificate should not be interpreted as legal confirmation that a document satisfies the EDPB anonymity criteria. It is evidence of a structured and reviewable process, not a substitute for the contextual assessment itself.
Technology supports anonymisation but does not replace contextual assessment
One of the most important conclusions from the EDPB Guidelines 02/2026 is that anonymisation cannot be reduced to a single technical function.
Software can:
- detect personal and sensitive information
- automate repetitive work
- permanently remove selected information
- apply consistent rules
- record the history of the process
However, the organisation must still assess the context in which the data will be used. The No Record Isolation, No Linkage and No Inference criteria require organisations to consider not only what has been removed, but also what remains in the document and what additional information may be available to the recipient.
A mature anonymisation process should therefore combine technology, predefined rules, human control and re-identification risk assessment.
Review your anonymisation process with Bluur
If your organisation still anonymises documents manually, the draft EDPB guidance is a useful opportunity to review whether the current process is repeatable, controlled and properly documented.
Bluur® combines automated information classification, configurable anonymisation schemes, manual verification, permanent redaction and process history in one environment.
Instead of testing the system only on an artificial example, start with a real document used by your organisation: a contract, HR document, report, application or another file that currently requires manual anonymisation.
Try Bluur® and see which identifying and sensitive information the system detects automatically before you decide what should remain in the final version of the document.
The goal of effective anonymisation should not simply be to create a document that looks anonymous. It should be to reduce the realistic possibility of identifying an individual from the information that remains.
Frequently asked questions about EDPB Guidelines 02/2026
Are EDPB Guidelines 02/2026 final?
No. As of September 2026, Guidelines 02/2026 are open for public consultation until 30 October 2026. The final version may therefore differ from the current draft.
What are the three EDPB anonymisation criteria?
The framework uses three criteria: No Record Isolation, No Linkage and No Inference. Together, they help assess whether a person can still be singled out, connected with other data or have information inferred about them.
Is anonymised data subject to the GDPR?
Information that has been effectively anonymised may fall outside the scope of the GDPR. However, the processing performed to achieve anonymisation takes place on personal data and is therefore subject to the GDPR while the process is being carried out.
Can anonymisation software guarantee GDPR compliance?
No software can replace the organisation’s legal and contextual assessment of whether information is genuinely anonymous. Technology can detect data, apply rules, remove selected information and document the workflow, but the organisation must still assess the risk of identification in the specific context in which the data will be used or shared.